Friday, 28 October 2022

Should the EU Ban the Real-Time Use of Remote Biometric Identification Systems for Law Enforcement Purposes?


Asress Adimi Gikay (PhD)

Senior Lecturer in AI, Disruptive Innovation, and Law

Brunel Law School & Brunel Centre for AI(London, UK)

Twitter: @DrAsressGikay

Photo credit: Irbsas, via Wikimedia commons


The Call for Ban on Real-Time Remote Biometric Identification System

It has been around two years since the European Commission introduced its Draft Artificial Intelligence Act ("EU-AIA), which aims to provide an overarching AI safety regulation in the region. The EU-AIA's risk-based approach has been severely criticised mainly for failing to take a fundamental rights approach to regulate AI systems. This post focuses on the EU-AIA's position on the use of Real-Time Remote Biometric Identification Systems (RT-RBIS) by law enforcement authorities in public spaces, which continues to cause the most controversy.  

The EU-AIA defines RT-RBIS as a "system whereby the capturing of biometric data, the comparison and the identification all occur without a significant delay" [EU-AIA Art. 3(37)]. The regulation covers the real-time processing of a person's biological or physical characteristics, including facial and bodily features, living traits, and physiological and behavioural characteristics, through a digitally connected surveillance device. The most commonly known RT-RBIS is facial recognition technology (FRT)—a process by which an AI software identifies or recognises a person using their facial image or video. The software compares the individual's digital image captured by a camera to an existing biometric image to estimate the degree of similarity between two facial templates and identifies a match. In the case of real-time systems, capturing and comparing images occur almost instantaneously.   

As EU institutions, Member States, and stakeholders continue to discuss the EU-AIA, there is growing dissent against the use of RT-RBIS for law enforcement purposes in publicly accessible spaces. In 2021, the European Parliament invited the Commission to consider a moratorium on the use of this technology by public authorities on premises meant for education and healthcare. In response to the EU Council's latest proposed revision of the EU-AIA, on October 17, 2022, 12 NGOs wrote a letter to the EU Council reiterating the need to prohibit the technology unconditionally.  


The Risk Posed by the Technology

RT-RBIS poses multiple risks that might jeopardise individual rights and citizens’ overall welfare.

As the technology is still evolving, there remains the risk of inaccurate analysis and decisions made by the system. In the United States, police have used FRT to apprehend individuals suspected of a crime where multiple instances of mistaken identification led to wrongful arrests and pre-trial incarcerations. In one example, a Black American wrongly identified by a Non-Real Time FRT for suspicion of shoplifting, resisting an arrest and attempting to hit a police officer with a car spent eleven days in jail in New Jersey. Between January 2019 and April 2021, 228 wrongful arrests were reportedly made based on FRT in the State of New Jersey. 

The deployment of RT-RBIS in public spaces could cause more significant harms compared to Non-Real time biometric identifications systems. These harms include missing flights, false arrests, and prolonged and distressing police interrogations that have adverse socio-economic and psychological effects on law-abiding members of society. 

RT-RBIS could also be applied discriminatorily, disproportionately targeting specific groups. In a 2019 study, researchers have found that FRT falsely identifies "Black and Asian faces 10 to 100 times more often than white faces." False positives were found to be between "2 and 5 times higher for women than men." Whilst an ethical and inclusive machine learning programme could alleviate this, the potential for discriminatory application of the technology cannot be ignored. In the UK, the existing policing practice has been criticised for subjecting ethnic minorities to disproportionate stops and searches. Indeed, the police should not be allowed to use technology to maintain similar stereotypical practices.

Lastly, RT-RBIS could continue to normalise surveillance culture and increase the infrastructure for it. Public spaces such as airports, train stations, and parking lots could be equipped with cameras that law enforcement authorities could activate for live biometric identification in case of necessity. This could expose the public to the risk of state surveillance. The use of FRT to crack down on the exercise of democratic rights by authoritarian governments is becoming a common practice.  Currently, there is an ongoing legal challenge against Russia before the European Human Rights Court for mass surveillance of protests using FRT.

The risks highlighted above must be addressed seriously and comprehensively. However, is a complete ban on the use of the technology a reasonable solution? 

Qualified Prohibition and Fundamental Rights Approach under the EU AI Act

Due to the high risk to fundamental rights  posed by some AI systems, scholars have argued that the EU-AIA should take a fundamental rights approach in regulating these AI systems. As fundamental rights are given strong legal protection, any measure that interferes with them should meet three legal requirements:

Interference  with derogable rights is allowed for a narrowly defined, specific and legitimate purposes prescribed by law, and subject to the tests of necessity and proportionality.

The burden of proving the necessity and proportionality of interfering with fundamental rights lies with the authority seeking to interfere with such rights.

A court or a similar independent body determines whether the authority has met the threshold of its burden of justification.

These requirements involve a careful judicial balancing act. The EU-AIA's qualified prohibition of using RT-RBIS effectively adopts the same approach. 

First, the EU-AIA permits, by way of exception, the use of the technology for narrowly defined, specific, and legitimate purposes [EU-AIA Art. 5(1)(d)]. These purposes are, (i) the targeted searches for specific potential victims of crime, including missing children; (ii) the prevention of a specific, substantial and imminent threat to the life or physical safety of natural persons or a terrorist attack; and (iii) the detection, localisation, identification or prosecution of a perpetrator or suspect of a crime with a maximum sentence of at least three years that would allow for issuing a European Arrest Warrant. These are specific and legitimate purposes for restricting fundamental rights, depending on the context. 

Second, the relevant law enforcement authority must demonstrate that the use of the technology is justifiable against: (a) the seriousness, probability and scale of the harm caused in the absence of the use of the technology; (b) the seriousness, probability and scale of consequences of the use of the technology for the rights and freedoms of all persons concerned; and (c) the compliance of the technology's use with necessary and proportionate safeguards and conditions in relation to the temporal, geographic and personal limitations[EU-AIA Art. 5(2)-3]. The authority proposing to use the technology bears the burden of justification.

Third, the relevant law enforcement authority must obtain prior express authorisation from a judicial or a recognised independent administrative body of the Member State in which the technology is to be used, issued upon a reasoned request. If duly justified by urgency, the police may apply for authorisation during or after use [EU-AIA Art. 5(3)].

The preceding analysis demonstrates that the EU-AIA does not give a blank cheque to the police to conduct spatially, temporally, and contextually unlimited surveillance. Despite the EU-AIA not explicitly employing fundamental rights language in the relevant provision, it entails a balancing act by courts, that must determine whether the use of RT-RBIS is necessary and proportionate to the purpose in question by considering multiple factors, including human rights. 


The Call for Categorical Prohibition is Unsound

The fear of increasing surveillance is one of the grounds for the heightened call for the complete prohibition of RT-RBIS. Nevertheless, viewed within the overall context, the envisioned use of the RT-RBIS under the EU-AIA does not significantly change the existing surveillance culture or infrastructure.   


Amid Corporate Surveillance Capitalism

Contemporary societies now live in massive corporate surveillance capitalism. Big Tech companies such as Facebook, Google, Twitter, Apple, Instagram, and many other businesses access our personal data effortlessly. They know almost everything about us— our location, addresses, phone numbers, private email conversations and messages, food preferences, financial conditions and other information we would prefer to keep confidential. Surveillance is the rule rather than the exception, and we have limited tools to protect ourselves from pervasive privacy intrusions. 

Whilst surveillance, if employed by law enforcement, is used at least in theory to enhance public welfare, such as prosecuting criminals and delivering justice, Big Tech uses it to target us with advertisements or behavioural analysis. The fear of law enforcement's use of RT-RBIS in limited instances is inconsistent with our tolerance for Big Tech corporate surveillance. This does not mean we must sink further into surveillance culture, but we should not apply inconsistent policies and societal standards, detrimental to the beneficial use of the technology.  


Minimal Change in Surveillance Infrastructure

 The deployment of RT-RBIS as envisioned by the EU-AIA is unlikely to change the current surveillance infrastructure significantly, where Closed-Circuit Television (CCTV) cameras are pervasively present. In Germany, in 2021, there were an estimated 5.2 million CCTV Cameras, most facing publicly accessible spaces. In the UK, there are over five million surveillance cameras, over 691 000 of which are in London. On average, a London resident could be caught  300 times on CCTV cameras daily. 

The police can access these data during the crime investigation, probably without needing a search warrant in practice. It is improbable that private CCTV camera owners refuse to provide access footage to the police due to a lack of a search warrant, unless they are involved in the crime or protecting others. At the same time, footage from these cameras play an instrumental role in solving serious crimes. However, the overall picture surveillance infrastructure would not significantly change; if it does, it is for a better public good.


Ethical Development and Use Guideline

The potential biases or disproportionate use of the technology against certain groups could be tackled by designing ethical standards for the development, deployment and use of AI systems. These guidelines include ensuring that the AI systems are bias-free before deployment and requiring law enforcement authorities to have clear, transparent and auditable ethical standards. The EU-AIA itself has several provisions to ensure this.


Maintaining the EU-AIA's Provisions on RT-RBIS

The use of RT-RBIS, as envisioned under the EU-AIA, does not fundamentally change the existing surveillance culture and infrastructure. Nor does it unreasonably increase the surveillance power of the state. On the contrary, a categorical ban would impede beneficial limited use. Therefore, the provisions of the EU-AIA governing the limited use of RT-RBIS by law enforcement authorities in publicly accessible spaces must be maintained. Stakeholders should resist the temptation to implement radical solutions that will harm societal interest, and focus on developing ethical guidelines for development, deployment and use of the technology. 

Monday, 24 October 2022

A boost for family reunification through the Dublin III Regulation? The CJEU on the right to appeal refusals of take charge requests


Mark Klaassen, Leiden University

Photo credit: DFID 

An unaccompanied minor has the right to appeal the refusal of a take charge request by the receiving Member State. This is the conclusion of the Court of Justice of the EU (CJEU) in the I. & S. judgment. The preliminary question posed by the District Court of Haarlem in the Netherlands was interesting from the outset because the Dublin III Regulation itself does not provide for such right to appeal. The take charge request procedure functions between two Member States and the individual asylum seeker is not a party to this procedure. The referring court essentially asked the CJEU whether the right to an effective remedy as protected by Article 47 of the Charter of Fundamental Rights obliges the Member States to provide for an appeal procedure against the refusal of take charge requests. In this blog, I discuss the reasoning of the Court and the implications for the application of the Dublin III Regulation.


The applicant is an Egyptian national who applied for asylum in Greece as an unaccompanied minor. His uncle lives in the Netherlands and the applicant would like to join him there as well. Based on the Dublin III Regulation, Greece made a take charge request to the Netherlands. As prescribed by Article 8(2), Greece deems that the Netherlands is responsible for handling the asylum request of the applicant. The Netherlands had refused the take charge request because it deemed that the applicant did not substantiate the existence of family ties with his uncle. Greece requested the Netherlands to reconsider the refusal, but this request was denied. The applicant and his uncle started proceedings against the refusal before the Dutch courts. The administrative appeal was declared inadmissible by the Dutch authorities because the Dublin III Regulation does not provide for a right to appeal the refusal of a take charge request. In the appeal against this, the referring court asked preliminary questions to the CJEU.


Based on Article 27(1) Dublin III Regulation, an asylum seeker has the right to appeal a transfer decision made by the sending State. But when the receiving State refuses a take over or take charge request, no transfer decision is made at all. The CJEU observes that even though Article 27(1) does not provide for a right to appeal the refusal of a take charge request by the receiving State, it does not exclude the possibility that such right to appeal exists. The Court refers to its earlier case law to conclude that the Dublin III Regulation is not only an instrument that functions between the Member States, but that it is also intended to afford rights to asylum seekers. Based on this assertion, the Court ruled in Ghezelbash that asylum seekers must be able to appeal the application of the criteria which determine which Member State is responsible to deal with an asylum request.


In the present judgment, the Court also applies this reasoning to the refusal of a take charge request of an unaccompanied minor. According to the Court, the legal protection of an asylum seeker may not be dependent on the acceptance or refusal of a take charge request (para 41).That would hinder the effectiveness of the right of the unaccompanied minor asylum seeker to be reunified with the family member lawfully residing in the receiving Member State (para 42). The Court holds that based on the right to an effective remedy, an asylum seeker has the right to appeal both the wrong application of the criteria, as well as the refusal of a take charge request (para 45). Furthermore, the right to appeal the refusal of a take charge request is also based on the right to respect for family life and the best interests of the child, as protected by respectively Article 7 and 24(2) Charter. An asylum seeker has the right to invoke the protection of these rights and therefore a procedure must exist to do so (paras 47-49). The family member residing in the receiving Member State does not have the right to appeal the refusal of a take charge request. The Court reasons that Article 27 does not grant appeal rights to the family member at all and therefore the family member also does not have the right to appeal the refusal of a take charge request.


This judgment makes it necessary for the Member States to provide for the possibility to appeal the refusal of a take charge request to the authorities of the receiving Member State. This is a novelty in EU asylum law. The Court does not give further guidance on this appeal procedure. In his Opinion, Advocate-General Emiliou observes that in the absence of concrete guidance in the Regulation itself, the appeal procedure falls within the procedural autonomy of the Member States, which is limited by the principle of effectiveness. The AG argues that this principle requires that the asylum seeker is informed of the reasons for the refusal of the take charge request. The AG deems it most appropriate if the authorities of the sending Member State inform the asylum seeker of the reasons of the refusal by the receiving Member State. Even though the Court has not made this explicit, in my view the reasoning of the AG is still applicable. Not informing the asylum seeker of the reasons for a refusal would undermine the effectiveness of the right to appeal because the asylum seeker would not know on what grounds the take charge request has been refused. Furthermore, the receiving Member State is already obliged to motivate the refusal of the take charge request to the sending Member State based on Article 5(1) Commission Regulation (EC) No 1560/2003. As the applicant is residing in the sending Member State at the moment that the take charge request is refused, it seems the most appropriate solution that the authorities of that Member State inform the applicant of the reasons of the refusal of the take charge request by the receiving Member State and the procedure to appeal this refusal. This, however, requires coordination between both Member States involved.


Having established that under the Dublin III Regulation an asylum seeker has the right to appeal the application of the criteria (Ghezelbash) and the refusal of a take charge request (I. & S.), a remaining question is whether an asylum seeker has the right to appeal against the refusal of a sending Member State to make a take charge request in the first place. In my view, the reasoning of the Court in I. & S. can be applied to that question as well. The Dublin III Regulation aims to provide concrete rights to asylum seekers and lists the criteria for determining the responsible Member State. An asylum seeker, however, is dependent on the sending Member State to make a take charge request. If the sending Member State simply refuses to make a take charge request, for whatever reason, the Dublin III Regulation does not provide the asylum seeker the possibility to appeal against this refusal. In my view, even though Article 27 Dublin III Regulation only grants the right to appeal a transfer decision, reading the criteria from the Regulation as rights for asylum seekers implies that refusing to apply the criteria would undermine the right of the asylum seeker to be transferred to a Member State where a family member is legally present. For this reason, asylum seekers must be able to challenge the refusal to make a take charge request.


The reasoning of the Court is also interesting in the light of the current negotiations regarding the reform of the Dublin system. Article 33(1) of the Proposal for a Regulation on asylum and migration management (COM(2020) 610 final) provides for a limitation of the right to appeal. It states that the scope of the legal remedy shall be limited to the risk of ill-treatment within the meaning of Article 4 Charter and the application of the criteria relating to family life. This proposal from the Commission is an attempt to limit the effects of the Court’s ruling in Ghezelbash. By repeating Ghezelbash and emphasising that the right to appeal is based on the Charter of Fundamental Rights in the I. & S. judgment, it seems unlikely to me that the Court would deem limiting the scope of the legal remedy to be lawful.


Considering that because of the structure of EU asylum law, family members with an asylum background often find themselves in different Member States, in practice the Dublin III Regulation can function as an instrument to bring families together. By placing family ties at the top of the pyramid of criteria in the Dublin system, this was also the intention of the EU legislature. The judgment of the CJEU in I. & S. makes clear that a refusal of a take charge request may violate fundamental rights and therefore a legal remedy must be made available by the Member States. This gives asylum seekers an extra tool to enforce the application of the Dublin criteria to reunite with family members.  

Saturday, 13 August 2022

To Use or Not to Use the European Digital Identity Wallet: Data Protection issues in the ongoing legislative debate


Alessandra Fratini and Giorgia Lo Tauro – FratiniVergano, European Lawyers

Photo credit: Martin Firrell, via Wikimedia Commons

Introduction

On 3 June 2021, in the context of the review of the eIDAS Regulation, the Commission proposed to establish a framework for a European Digital Identity, including a ‘European Digital Identity Wallet’ (the EUDI Wallet, or simply Wallet). Considered as the main innovation of the Proposal, the Wallet intends to respond to the growing digitisation of cross-border public and private services and remove barriers for citizens, residents and businesses when using online services across the EU. The evaluation of the eIDAS Regulation, in fact, had revealed a number of shortcomings (e.g., non-coverage of electronic attributes, such as medical certificates or professional qualifications, which makes cross-border legal recognition of such e-credentials difficult; data protection concerns as regards identity solutions offered by social media providers and financial institutions, which fall outside the scope of the Regulation; no possibility to limit the sharing of identity data to what is strictly necessary for the provision of a service), which the proposed EUDI Wallet seeks to address.

The declared aim of the Proposal is to enhance users’ control over their own data. At the outset, the Proposal is set in the context of the 2020 Commission Strategy ‘Shaping Europe’s digital future’, aimed at strengthening trust in the online world by giving consumers greater control and responsibility over their own data, in line with the Digital Europe that “puts people at the centre”. The Commission further acknowledges that giving citizens and residents full confidence that the European Digital Identity framework will offer everyone the means to control who has access to their digital identity, and to which data exactly, requires a high level of security with respect to all aspects of digital identity provisioning, including the issuing of EUDI Wallets. In this respect, the Explanatory Memorandum that accompanies the Proposal notes that the latter ‘supports the implementation of GDPR (2016/679) by putting the user in control over how the personal data is being used. It provides a high level of complementarity with the new Cybersecurity Act and its common cybersecurity certification schemes’. Finally, the proposed “measures are designed to fully comply with the data protection legislation”.

However, the legislative debate on the Proposal has brought up potential data protection issues associated to the use of the EUIDI Wallet. This contribution, after a brief recap of the main features of the Wallet, reviews how those potential issues have been addressed at the current stage of the legislative debate, in particular in the European Parliament.

The main features of the European Digital Identity Wallet

The EUDI Wallet is defined in Article 3.1.42 as a ‘product and service that allows the user to store identity data, credentials and attributes linked to her/his identity, to provide them to relying parties on request and to use them for authentication, online and offline, for a service in accordance with Article 6a; and to create qualified electronic signatures and seals’. It is basically an app, that will enable citizens to digitally identify themselves online and offline, confirm certain personal attributes (age, for example), store and manage identity data and official documents (diplomas, driving licenses, medical prescriptions, …) in electronic format, with the click of a button on their phone.

In the Commission’s intentions, the EUDI Wallet provides simplification and convenience for EU citizens, residents and businesses when dealing with national administrations and other service providers. While some are already using digital wallets for storing certain data, the EUDI Wallet will be available to everyone in the EU and grant users full control over their data, allowing them to choose what they share with third parties (for example, age when buying alcohol, without revealing their identity or other details) and keep track of such sharing. Choice and control over their data will enhance users’ trust in the digital environment, for the sake of the digital single market as a whole. Recital 28 recalls the principle of data minimisation, while recital 29 sets forth selective disclosure as a basic design feature of the Wallet, “thereby reinforcing convenience and personal data protection including minimisation of processing of personal data”.

The proposed new Articles 6a to 6d, under the title ‘Electronic Identification’ (Section I, Chapter II), are dedicated to the Wallet. Under Article 6a, Member States are required to issue a EUDI Wallet under a notified eID scheme to common technical standards following compulsory compliance assessment and voluntary certification within the European cybersecurity certification framework, as established by the Cybersecurity Act. The Wallets 1) are envisaged for ensuring natural and legal persons in the EU a secure, trusted and seamless access to cross-border public and private services; 2) shall be issued by a Member State, under a mandate of a Member State or independently, but recognised by a Member State; and 3) shall enable users to securely request and obtain, store, select, combine and share, in a manner transparent and traceable by them, the necessary legal person identification data and electronic attestation of attributes to authenticate online and offline in order to use online public and private services - and to sign by means of qualified electronic signatures. The certification is without prejudice to the GDPR, in the meaning that personal data processing operations relating to the Wallet can only be certified pursuant to Articles 42 and 43 GDPR.

Article 6a.4 provides that the Wallet shall: (b) ensure that trust service providers cannot receive any information about the use of the attributes; (c) grant a ‘high’ assurance level; (d) provide a mechanism to ensure that the relying party is able to authenticate the user and to receive electronic attestations of attributes; (e) ensure that the person identification data uniquely and persistently represent the natural or legal person associated with it. Article 6a.7 establishes the full control of the user over the Wallet and adds that the issuer shall not collect, nor combine, data not necessary for the provision of the Wallet services. Article 10a further includes provisions to handle security breach of the Wallets.

In addition, the Proposal contains provisions to ensure the unique and persistent identification of natural persons in Article 11a. The Explanatory Memorandum clarifies that this concerns cases where identification is required by law such as in the area of health, in the area of finance to discharge anti-money laundering obligations, or for judicial use. For this purpose, Member States will be required to include a unique and persistent identifier in the minimum set of person identification data referred to in Article 12.4(d).  

The specifications and standards of the Wallet will be developed in parallel with the legislative process- and in alignment with its outcome. In fact, to avoid fragmentation and barriers due to diverging standards, the Commission adopted a Recommendation setting up a structured process of cooperation between Member States, the Commission and, where relevant, private sector operators to develop a Toolbox, which should in turn lead to a technical Architecture and Reference Framework (AFR), a set of common standards and technical specifications and a set of common guidelines and best practices as a basis for implementing the European digital identity framework. According to the schedule for the implementation of the Recommendation, the Toolbox shall be published by the end of October 2022 and updated following the outcome of the legislative process. The eIDAS expert group, tasked as main interlocutor for the purposes of implementing the Recommendation, adopted in February 2022 an Outline providing a summary description of its understanding of the EUDI Wallet concept, including the objectives of the new tool, the roles of the actors of the ecosystem, the Wallet’s functional and non-functional requirements, the potential building blocks.

The use of the EUDI Wallet: potential data protection issues

From a data protection perspective, recital 6 of the Proposal states that the GDPR applies to the processing of personal data in the implementation of the proposed Regulation. It also adds that specific safeguards are needed to prevent potential combinations between personal data relating to services falling within the scope of the Regulation and personal data from other services.

The EDPS, in its Formal Comments on the Proposal of 28 July 2021, was the first to raise some concerns in this respect, noting that ‘[w]hether the specific safeguards are sufficient depends mainly on the technology to be used in implementing the proposal’. It praised the fact that the new Wallet gives users control over their data and appreciated a number of provisions (Article 6a.7 on selective disclosure; Article 6c.2 on the certification for certain requirements of the Wallet). However, in connection with the unique and persistent identifier to be used by Member States (Article 11a), the EDPS highlighted that this provision constitutes an additional category of data stored solely for the purpose of facilitating the usage of the Wallet - and such an ‘interference with the rights and liberties of the data subject is not necessarily trivial’. Recalling that in some Member States (Germany, for example) unique identifiers have been considered unconstitutional due to a violation of human dignity, he recommended exploring alternative means to enhance the security of identity matching.

In other words, the EDPS appears to say that facilitating the use of the Wallet shall be adequately weighted against the risks for the rights and liberties of the data subjects. When identifiers are used, the strictest legal and technical safeguards must be applied, with adequate (regulatory and technological) prevention mechanisms.

Following publication of the Proposal, some have questioned whether the EUDI Wallet actually supports the principle of data minimisation set out in Article 5.1(c) GDPR (personal data shall be ‘adequate, relevant and limited to what is necessary in relation to the purposes for which they are processed’). It is true that recital 28 recalls the respect of data minimisation by large online platforms when they accept the Wallet for the purpose of users’ access to private services, that recital 29 presents this principle, in conjunction with that of selective disclosure, as a basic feature of the Wallet, and that Articles 6a.7 and 12b.3 reflect it – which are all improvements of current eIDAS Regulation. However, the very compatibility with the principle is put in question by the minimum set of person identification data, which is part of the interoperability framework, in particular because the Proposal deletes the criteria under Article 12(3)(c) (‘it facilitates the implementation of the principle of privacy by design’) and (d) (‘it ensures that personal data is processed in accordance with Directive 95/46/EC’), and does not replace those with the corresponding references of the GDPR.

The committees of the European Parliament involved in the legislative procedure have all flagged issues for the rights and freedoms of individuals (see ITRE draft report of 31 May 2022 and amendments published on 5 July 2022; IMCO draft opinion of 8 February 2022 and its amendments of 24 May 2022; JURI draft opinion of 29 April 2022; LIBE draft opinion of 19 May 2022 and its amendments of 13 June 2022).

The amendments proposed in the ITRE draft report, as explained by Rapporteur Jerković, are focused on four areas: cybersecurity, with the introduction in Article 6a of the explicit requirement that the EUDI Wallet ensures ‘cybersecurity by design’ (AM. 68, 405 and 407); data protection, with the strengthening of prevention mechanisms and alignment with the GDPR, for example by introducing in Article 6a (AM. 70) and in recital 29 (AM. 21) the ‘privacy by design principle’ as a standard design feature of the EUDI Wallet; governance, with the introduction of a new Chapter IVa (AM. 131) on the tasks and coordination of national authorities; digitalisation of public services, with further support to the cross-border application of the ‘once only principle’ (AM. 7) to reduce administrative burden.

On the interplay with the GDPR, AM. 8 (recital 6) proposes that the new Regulation should ‘complement Regulation (EU) No 2016/679 by laying down specific safeguards’. Accordingly, its specific rules ‘should not be regarded as lex specialis’ to the GDPR. Under AM. 158, in ‘case of conflict Regulation (EU) No 2016/679 takes precedence over this Regulation’. Also, the amendments to Article 12.3(c) (AM. 97) and the new Article 5a (AM. 38) require that processing of personal data shall be in accordance with the GDPR, while AM. 22 adds to recital 29 that ‘[i]n general, insofar as personal data are concerned, the processing of such data should rely upon the grounds for processing provided in Article 5(1)(c) of Regulation (EU) 2016/679’ and the proposed new Article 6a.6a makes it clear that ‘the use of the European Digital Identity Wallets shall be on a voluntary basis’ (AM. 69): in other words, consent is key.

For the rest, the amendments that are relevant from a privacy/data protection perspective can be grouped under four clusters. The first cluster concerns amendments upholding users’ control via the principle of minimisation and selective disclosure, such as those aiming at: reducing to the minimum users’ digital footprint when using the internet via the Wallet (AM. 8, recital 6); embedding transaction history into the design of the EUDI Wallet, active by default, so that users can track all transactions executed through it (AM. 9, new recital 6a); introducing the so-called ‘Zero Knowledge Proof’ (ZKP), which allows verification of a claim without revealing the data that proves it, based on cryptographic algorithms (AM. 10, new recital 6b, AM. 31, new Article 3.1.5a, AM. 160, new recital 6a); adding to the definition of the Wallet the possibility for users to not only store, but also ‘manage’ their identity data credentials and attributes, and to use them for identification and authentication online and offline to access public and private services (AM. 32, Article 3.1.42, AM. 599, new Article 45e.1a); confirming the principle of minimisation, not only as regards the information requested from the user via the EUDI Wallet (AM. 20, recital 28), but also by requiring that relying parties ‘minimise the processing of personal data’ (AM. 57, Article 6a.4d). As explained in LIBE’s statement in connection with its amendment to Article 6a.4a.3 (LIBE AM. 8), the success of the EUDI Wallet will depend on ‘citizens making informed decisions on the information they share with relying parties’.

The second cluster includes amendments focusing on data protection by preserving confidentiality and privacy when using the Wallet, such as those establishing the ‘privacy by design principle’ as a standard feature of the EUDI Wallet: AM. 21 (recital 29) and AM. 70 (Article 6a.7) require it in order to reinforce user control, while the latter introduces also provisions to make it technologically impossible for issuers of the Wallets and of electronic attestation of attributes, as well as for relying parties, to receive any information on the use of the Wallet or its attributes without the users’ consent. This is also in line with amendments to Article 6a.4e tabled by IMCO and LIBE: IMCO proposes that data shared for person identification ‘shall work on the principle of pair-voiced anonymity, and the interactions with a user from one relying party to another relying party shall not be traceable to the same individual and combinable’ (IMCO AM. 89); LIBE requires ‘unlinkability’ and non-traceability (LIBE AM. 10), as does ITRE (AM.383, Article 6a.4d), and the implementation of the EUDI Wallet’s essential functions ‘in a privacy-preserving manner’ (LIBE AM. 3, recital 29). Along the same lines, AM. 38 introduces a new Article 5a on ‘protection of personal data’, to the effect that ‘processing of personal data shall be carried out in accordance with the GDPR and in particular by implementing principle of privacy by design and by default’. Similarly, AM. 158 clarifies that ‘[d]ata protection by design and by default, as well as data minimisation, as foreseen in Regulation (EU) 2016/679, should be leading principles in the set-up’ of the EUDI Wallet. AM 15 (recital 11) takes issue with the use of biometric data, specifying that using biometrics ‘to identify and authenticate should not be a precondition’ for using the Wallet and that those data should not be stored in the cloud. The same amendment requires the user’s explicit consent for storing information from the Wallet in the cloud. Similar amendments are tabled by LIBE (LIBE AM. 2, recital 11). Amendments calling for pseudonymisation and/or anonymisation suitably fit into this cluster: ITRE requires that the EUDI Wallet ensures that ‘the relying party is able to anonymously authenticate the user and to receive electronic attestation of attributes’ (AM. 57, Article 6a.4d) and refers to the right to pseudonymity (AM. 238, AM. 286, AM. 521, AM. 526); JURI proposes that ‘the use of services anonymously or under a pseudonym should be allowed and should not be restricted by Member States’ (JURI AM. 6, recital 28, and AM. 13, Article 5); LIBE specifies that the use of pseudonyms shall always be an option in all cases where full identification is not legally mandated (LIBE AM. 5, Article 5).

The third cluster concerns amendments to the provisions on the disputed unique and persistent identifier. Not only ITRE (AM. 92-94, AM. 202-204, AM. 492, 495-500), but also LIBE (LIBE AM. 12) and IMCO (IMCO AM. 24) delete the Proposal’s references to a such an identifier. LIBE’s justification explains that such an identifier would be illegal or unconstitutional in some Member States, it is not considered the least intrusive method for the purpose of uniquely identifying an individual, and finally Article 11a is not needed as the existing interoperability framework of identification schemes (Article 12.4 (d)) already entails a unique representation of an individual for cross-border cases (LIBE AM. 12). For this purpose, LIBE proposes to also amend Article 12 accordingly (AM. 13).

The fourth cluster of relevant amendments focuses on data security, with provisions mostly related to cybersecurity in the design of the Wallet. The main innovation is the above-mentioned addition of ‘cybersecurity by design’ in Article 6a.6 (AM. 68), which also requires necessary security functionalities ‘to offer resistance to skilled attackers, ensure the confidentiality, integrity and availability of the content’ of the Wallet. Other amendments underline data security, such as AM. 14 (recital 29) requiring common standards and technical specifications ‘to adequately increase the level of IT security, strengthen robustness against cyber-attacks and thus significantly reduce the potential risks of ongoing digitalisation for citizens and businesses’, while AM. 86 replaces the title of Article 10 with “Security breach of electronic identification schemes for cross-border authentication”.

The synthetic overview above shows how the European Parliament committees (ITRE and LIBE in particular) have this far addressed data protection issues associated to the use of the EUDI Wallet. However, the amendments are still to be voted upon and, while the ones reviewed above appear to improve the Proposal from a data protection perspective, others retain some ambiguities or do not fully capture instances that could properly reduce data protection concerns. It is worth recalling, in this respect, LIBE’s warning that the Proposal, as such, is able to lead towards ‘the creation of a like social-credit system that would determine the mass surveillance and control of all Europeans, which must not be accepted. EU was envisioned as an “area of freedom” and efforts must be continued to keep it as such’ (short justification, p. 4 LIBE draft opinion).

Privacy issues in a broader context

In addition to the above, and in a broader perspective, reference shall be made to AM. 40 (Article 6a.2.c), providing for the EUDI Wallet to be issued (instead of ‘independently but recognised by a Member State’) ‘by an organisation established in the Union’. The amendment triggered a discussion at the ITRE meeting of 14 June 2022, fuelling confusion over a feared re-definition of the role of Member States when it comes to the issuance of the Wallets. While the Rapporteur ruled out any intention to redefine the role of Member States in this respect, the issue is not trivial (to echo the EDPS), given that the implied aim of a new harmonised digital identity framework at European level is to strengthen the role of public intervention over that of strong private actors on the Internet, which is in turn linked to the extent of users’ effective control over their data. Defining the limits of State intervention on digital identity is a delicate exercise: a too limited role would expose users’ identity data to the very threats that the Proposal aims to address, while a too large role would entail risks of mass surveillance of citizens’ behaviour, contrary to the very funding values on which the EU is built. Concerns in both directions have been raised in the debate and some emphasised the need to consider digital identity as a tool serving individuals in their relationship with States and society, and not the other way around, noting that, in the current geopolitical context, it shall reflect the digital identity of the EU itself.

Emblematic in this respect, if one of the objectives of the Proposal is to give users effective control over their own data, are the LIBE (LIBE AM. 32, recital 11; LIBE AM. 57, recital 29; LIBE AM. 147, Article 6a.7) and ITRE (AM. 239 and AM. 332) amendments to allow the revocability of data entered in the Wallet:; then followed by some MEPs within ITRE: the prospect of using the Wallet, and enjoying the simplifications it promises to bring, can only convince if users are given actual control over the data in-and-out their Wallet and dangers of - public or private – control are fenced off.

At this stage, it will be the task of the co-legislators to strike the right balance and put individual rights at the centre of the digital transformation in the EU.

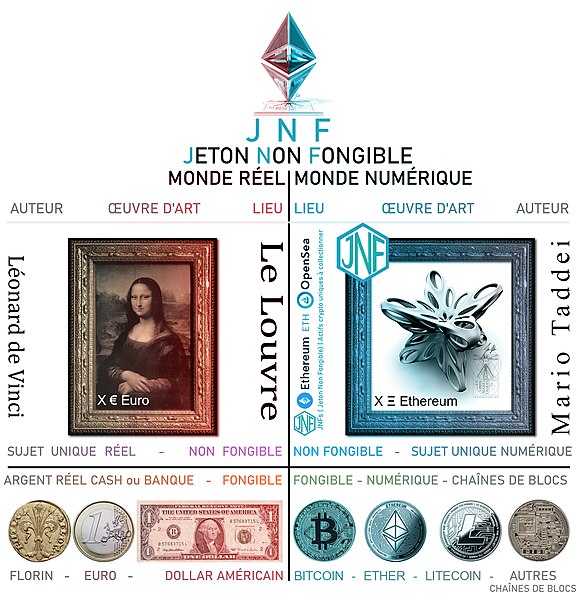
When art goes virtual: what status for collectible NFTs under the current EU Anti Money-Laundering regime?


Anna Mosna, postdoctoral researcher at the Leuven Institute of Criminology (LINC), KU Leuven and Giulio Soana, Ph.D. candidate at Luiss University and KU Leuven


Photo credit: Mario Taddei, via Wikimedia Commons


Introduction


What if we told you that you can buy a digital image of an ape wearing a crown and heart-shaped glasses for two and a half million? Well, you may find this a bit pricey. This does, however, not seem to be a common feeling as images of funny looking apes have sold, over and over, at stellar prices. This specific project is called Bored Ape Yacht Club (BAYC) and features 9999 images of apes, each one slightly different from all the others. The combined value of the collection is reportedly a dizzying 2.9 billion dollars. This is just one of the many non-fungible token (NFT) ventures that have been flourishing in the last few years.


Trade in NFTs represents a new market that features virtual goods at skyrocketing prices and apparently little regulation and oversight. With sums of this magnitude at stake, it is inevitable to think about the repercussions of this new market for illicit financial flows control. And indeed, NFTs receive increasing attention in the financial integrity arena. In its ‘2022 Crypto Crime Report’, Chainalysis, one of the most renowned crypto analytics companies globally, identified a growing relevance of NFTs to pursue money laundering and wash trading. This risk was confirmed by the latest virtual assets (VA) report published by the Financial Action Task Force (FATF) in June 2022. There, NFTs have been recognised as one of the key market developments to keep under close watch.


What are NFTs?


Before delving into the intricacies of the anti-money laundering regulation, a brief introduction on what NFTs are, is in order. Non-fungible tokens are one of the latest implementations of blockchain. They exploit blockchains’ immutability and decentralization to create unique, unalterable, and programmable tokens that can be freely traded among the participants of the network. On the one hand, blockchain’s publicity and immutability safeguards the authenticity and uniqueness of the token while allowing anyone to verify it by, simply, accessing the ledger. On the other hand, blockchain’s decentralization means that there is no single entity that can unilaterally modify or control the status of the token once it is created. The token can both be a digital representation of a physical or digital asset–as a work of art, a song, or a ticket to a concert–or solely exist as a digital token. In this latter case, the value is determined exclusively by the characteristics intrinsic to the token, its rarity, in case of a token series like BAYC, being an important factor.  


While NFTs may be used in multiple ways–spanning from the amelioration of the supply chain to the metaverse–there is one type that presents a particularly high risk in terms of financial integrity as it is completely decoupled from any pre-existing digital or physical value: digital art, also referred to as collectible tokens, digital collectibles or crypto-collectibles. These are, furthermore, the prime and largest implementation of this technology.


Sharing characteristics with both virtual currencies and works of art, collectible NFTs are difficult to frame into a specific category, difficult to regulate and, thanks to their dynamism, prone to misuse for criminal purposes–including money laundering. It is therefore interesting to examine where–if anywhere at all–NFTs can be positioned among the sectors currently covered by the anti-money laundering (AML) framework applicable in the European Union (EU).


The progressive extension of anti-money laundering rules – what about NFTs?


Over the years, anti-money laundering rules have been continuously expanded to address a growing array of laundering tactics. Control and regulation instruments have come to cover alongside service providers and intermediaries in traditional fields, such as the banking sector, also other entities offering financial services, such as the insurance sector, or operating outside the spectrum of financial businesses, such as the real estate sector. Increasing awareness of the potential misuse for the purposes of money laundering and terrorism financing of virtual currencies, due to the anonymity they ensure, and of art transactions, nurtured by the speculative nature of prices at which they are carried out, has triggered a similar extension.


Among others, these risks have been highlighted, in the FATF Updated 2021 Guidance for a risk-based approach to virtual assets and virtual asset service providers and, regarding the art market, already in the FATF 2006 Study on trade-based money laundering. Likewise, consciousness of these concerns is reflected in the most recent EU legal instruments in matters of anti-money laundering. The rules enshrined in Directive (EU) 2015/849 on the prevention of the use of the financial system for the purposes of money laundering or terrorism financing as amended by Directive (EU) 2018/843 (Fifth AML Directive) now apply also to entities engaged in exchange services between virtual currencies and fiat currencies or trading in works of art.


As obliged entities, virtual currency service providers and art market actors must carry out customer due diligence (CDD) that includes know-your client procedures (KYC). As a result, customers and beneficial owners must be identified and their identity verified. CDD also requires a continuous assessment of the business relationship considering its purpose and intended nature. If these compliance measures cannot be carried out, virtual currency service providers and art professionals must refuse to carry out the transaction. They further have an obligation to submit suspicious transaction reports to their national Financial Intelligence Unit (FIU) and to keep documents acquired in compliance with their due diligence duties along with supporting evidence and transaction records for at least five years after the end of the business relationship or after the end of the occasional transaction. These due diligence duties and record keeping obligations are intended to ensure more transparency and better traceability of transactions and to thereby more effectively prevent and, possibly, enforce laundering activities occurring in the trade with virtual currencies and in the art market.


The considerations that led to the inclusion of these two sectors within the scope of application of AML rules suggest that there is a comparable need to do the same with the trade in NFTs. NFTs are similar in nature to virtual assets and, at times, to works of art. These tokens even combine and magnify the respective risk factor of each of these two categories. Like virtual assets, NFTs are immaterial and can be exchanged globally and instantaneously in a pseudonymous fashion. Like works of art and collectibles, NFTs have a variable and subjective price that can be artificially inflated.


Against this background, the question about the extent to which existing AML rules are already applicable to the trade in NFTs imposes itself. The answer, which is likely to differ according to the use made of the NFTs considered, will depend on the possibility to actually subsume NFTs under the concept of goods whose trade is already regulated. In short: virtual assets, virtual currencies or works of art.


Non-fungible tokens as virtual assets and virtual currencies


The link between NFTs and virtual assets is an obvious one. With virtual assets, NFTs share the technology they both predominantly employ, the blockchain. Most NFT projects are even rooted in an infrastructure–Ethereum–that issues a coin–the Ether–that is classified as a VA. It is, then, natural to wonder if these tokens are themselves virtual assets and, thus, if they fall within the scope of the same financial integrity regulation as VAs.


Virtual assets have been, since 2014, object of a progressively stringent regulation. Through ad-hoc guidelines, the FATF has extended to numerous players in the VA world–such as exchangers, wallet providers–registration and compliance duties. According to the FATF glossary, virtual assets are ‘a digital representation of value that can be digitally traded, or transferred, and can be used for payment or investment purposes’. Notwithstanding the distinct similarity to such assets, according to the FATF, NFTs are, in principle, not considered to be virtual assets. As provided by the above-mentioned 2021 Guidance, ‘[d]igital assets that are unique, rather than interchangeable, and that are in practice used as collectibles rather than as payment or investment instruments […] depending on their characteristics, are generally not considered to be VAs under the FATF definition’.


This exclusion does however not imply that NFTs are entirely exempt from the application of anti-money laundering rules. As the FATF Guidance clarifies, this definition of ‘virtual assets’ must be interpreted broadly and functionally–meaning: through the analysis of the concrete function of the analysed asset. First, the FATF specifies that the exclusion only covers tokens that are used as collectibles. If NFTs are used in practice as means of payment or investment, they would still fall within the definition of VA and, one could add, also within that of ‘virtual currencies’ as coined by the Fifth AML Directive. The Directive defines virtual currencies as ‘a digital representation of value that is not issued or guaranteed by a central bank or a public authority, is not necessarily attached to a legally established currency and does not possess a legal status of currency or money, but is accepted by natural or legal persons as a means of exchange and which can be transferred, stored and traded electronically’.


Second, the exclusion of NFTs from the scope of the VA regulation does not preclude collectible NFTs from falling, depending on their concrete use, within a different category of regulated asset. This would, for instance, be the case where NFTs are digital representations of other financial assets that are already covered by FATF standards. Also in this case, the AML regime governed by the Fifth AML Directive may apply.


Non-fungible tokens as works of art?


What if NFTs are not used as means of payment or investment, but indeed only used as collectibles? Parallels between NFTs and works of art are, unlike those between NFTs and VAs, not structural but content-related. Collectible NFTs encapsule (digital) art. Can they therefore be defined as ‘works of art’ within the meaning of the Fifth AML Directive?


The Fifth AML Directive does not provide for a definition of the concept of ‘works of art’. Even without considering digital contents, this raises the question as to whether only those who trade in so-called ‘fine art’ are subject to the EU AML regime or whether these rules apply also to those who trade, more generally, in cultural objects including, hence, antiquities. As was foreseeable, national implementation laws reflecting different sensitivities towards the need to protect cultural heritage have based their provisions upon different understandings of what ought to be considered a work of art.


Member States with considerable wealth of antiquities and a long-standing tradition of strict cultural heritage protection laws, such as Greece or Italy, have adopted a broad notion of works of art and extended national anti-money laundering rules to those trading in fine art and to those trading in antiquities. States that are mainly market countries for cultural objects, such as Germany and the United Kingdom–where the Fifth AML Directive was implemented before Brexit–have opted for a narrower concept of ‘works of art’. Aligning their definition to the one provided in their respective laws on value added tax, they apply their AML regime to those who trade in paintings, drawings, engravings, sculptures and other objects that can be entirely executed by hand. The trade in antiquities is included insofar as the antiquities traded qualify as paintings, drawings, engravings, sculptures. This understanding excludes antique furniture, coins and stamps collections from the concept in question.


A workable definition of ‘works of art’ based on the lowest common denominator that has informed national implementations comprises objects that are individually conceived and executed by a person by hand or, one could reasonably add, with the help of different techniques and technologies, as long as the creative process remains human-initiated. Revolving around the two focal points of human creativity and uniqueness this definition excludes objects that are the result of automated reproduction of a potentially unlimited series of identical items. The question now is whether, applying this criterion to digital art, it would allow to identify collectible NFTs, such as those containing an image of an algorithm-generated Bored Ape, as a work of art as envisaged by the Fifth AML Directive.


The societal perception of NFTs such as the Board Apes is already that of iconic images, of art. This is confirmed by the fact that collectible NFTs are sold in digital galleries and at digital auctions–as was the case with the NFT ‘Everyday: The First 5000 Days’ by Mike Winkelmann, known as Beeple, that was sold for 69.3 million dollars with fees at Christie’s in early 2021–and, most importantly, by the fact that many artists that have been creative outside the Web3.0–Marina Abramović being an eminent example–consider this kind of NFTs as a new, attractive form of artistic outlet.


From a legal standpoint, the concept of ‘work of art’ included in the Fifth AML Directive seems equally to allow for such an inclusion: NFTs are by definition unique and those who are relevant as collectibles–let’s think about the Bored Ape collection, about Beeple’s ‘Everyday: The First 5000 Days’ or about Marina Abramović’s ‘Hero 25FPS’–are the result of human ingenuity and creativity. That being said, as the concrete application of the AML regime designed by the Directive in question depends on national legal instruments implementing its provisions and given that many national laws, like the relevant German framework, identify works of art through lists of categories of objects, it is likely that legislative adjustments may be necessary at that level before the current AML rules are capable to govern the trade in collectible NFTs as well.


Concluding remarks


The general exclusion of collectible NFTs from the purview of the VA regulation does not equal an automatic exclusion of the trade in NFTs from the scope of application of AML rules. Depending on the concrete use that is made of NFTs, they may still be considered virtual currencies or fall within the scope of a different category of regulated assets. This is particularly meaningful in regions, like the EU, where a more stringent regulation than the one envisaged by the FATF has been adopted: it suffices to think of the application of the travel rule to unhosted wallets.


Furthermore, the EU AML regime extends also to the trade in works of art–a  category, as has been argued above, under which collectible NFTs could be subsumed. Collectible NFTs appear, indeed, to fulfil the basic requirements of ‘works of art’ as identified by laws implementing the Fifth AML Directive. An extension of the AML regime is therefore possible and, perhaps, not entirely inappropriate in light of the very nature of collectible NFTs: as digital art, they are susceptible to highly subjective, at times arbitrary price-setting. This feature is exacerbated when NFTs exist only as digital tokens. In that case, they do not have any relation to a pre-existing digital nor to a physical artistic expression that could act as a possible parameter for such pricing.


Wherever prices can be modified at will and single transactions exceed several millions of dollars–or euros, or pounds–there is an inherent and, arguably, quite sensitive risk of money laundering. Introducing regulation and control appears therefore to be a sensible consideration. As a matter of fact, the policy discourse surrounding NFTs of the last year shows how both the private and the public sector are eager to discuss such measures for the trade in NFTs. This also shines through the Proposal for a Regulation on markets in crypto-assets (MiCA) that is currently undergoing the ordinary legislative procedure. While it does not seem that NFTs will be included in the definition of ‘utility token’ nor, in principle, in the scope of application of MiCA–in line with their positioning regarding FATF standards–Recital 8b that has been newly added to the Proposal for the Regulation refers to the need to reflect on a separate legislative proposal of an EU-wide regulatory regime for NFTs.

Monday, 1 August 2022

Creating procedural obligations under EU law: a way forward to enhanced protection of fundamental rights in the field of migration?


Opinion of AG de la Tour in Joined Cases C, B (C‑704/20) and X (C‑39/21)

Alicja SÅ‚owik, Assistante de recherché, Centre d’études juridiques européennes (CEJE), Université de Genève

Photo credit: Abouttt, via Wikimedia commons


Striking a fair balance between the principle of national procedural autonomy and the necessity to guarantee effective judicial protection of rights derived from EU law has never been an easy task for the European Court of Justice (‘the ECJ’/’the Court’). Yet, the task becomes particularly complex when what is at stake is effective judicial protection of rights of fundamental nature.  How could the concern for protection of EU fundamental rights affect the application of national procedural rules? Can national rules limit the power of the judge to assess the lawfulness of detention of foreign national or would such a limitation lead to serious encroachment on the fundamental right to liberty? The recent Opinion of AG Jean Richard de la Tour in the Joined cases Staatssecretaris van Justitie en Veiligheid v. C, B (C‑704/20, ‘Case C, B’) and X v. Staatssecretaris van Justitie en Veiligheid (C‑39/21, ‘Case X’) concerning the issue of ex officio review of detention measures provides for precious insights on the possible answers to these questions.


Legislative background and facts of the Joined cases

The two Joined cases at hand concern the scope of powers of national judges to examine the lawfulness of detention of third country nationals. In EU law, such a detention may be exceptionally imposed with regard to asylum seekers or migrants staying illegally on the EU territory. Articles 15 to 17 of the Return Directive, 8 to 11 of the Reception Conditions Directive and Article 28 of Dublin III Regulation provide for legal basis and conditions pertaining to detention. It is thus by reference to these provisions that the judge examines the lawfulness of detention of third country nationals (‘TCNs’).

In the Netherlands, detention of foreign nationals is governed by administrative procedural law which does not allow national courts to examine the conditions of the lawfulness of detention of their own motion (ex officio). This means that it is impossible for a national judge to review detention measure on the grounds other than those relied on by the foreign national during the proceedings. Moreover, the judge cannot release the detainee even after having found that the detention is unlawful on grounds different than those put forward by the person concerned. The preliminary questions addressed by two Dutch jurisdictions: the Council at State (Raad van State) and the District Court in the Hague (Rechtbank Den Haag) related to the problem of compatibility of Dutch legislation with EU law, especially, with the right to an effective remedy and right to liberty.

The first case, C and B, concerned detention measures imposed with regard to two TCNs. The first individual concerned was put in detention for the purpose of determining the elements necessary for the examination of his application for international protection. The second applicant was placed in detention with the aim of securing his transfer to Italy in accordance with Dublin III Regulation. Both contested the detention orders before the District Court which ordered their release on the ground relating to the non-respect of the obligation of due diligence. Importantly, the argument concerning the non-respect of due diligence obligation was not raised by the detainees during the proceedings.

The Secretary of State brought an appeal against the judgements ordering the release of two foreign nationals before the Council of State. The two TCNs argued that, by virtue of EU law, the national jurisdictions had a duty to examine the lawfulness of detention measure of its own motion. Yet, as explained above, such an ex officio review of detention was impossible to perform under the Dutch legislation. In these circumstances, the Council of State decided to ask the ECJ for clarifications on the interpretation of Article 15, paragraph 2, of Return Directive and Article 9 of the Reception Conditions Directive in light of Article 6 of the Charter of Fundamental Rights of the EU (‘the Charter’) which guarantees the right to liberty.

The second case, X, concerned the application of the Return Directive. A TCN had been put in detention on grounds relating to the maintenance of public order. The applicant challenged the decision on the continuation of detention before the District Court. The judge again had doubts on the compatibility of Dutch legislation prohibiting the ex officio review of detention with EU law.


Opinion of the Advocate General

At the very beginning of the Opinion, the AG noticed that the role of the judge does not differ much depending on whether he assesses the lawfulness of the detention order or of the order on the continuation of detention (§68). Further, relevant provisions of Return Directive, Reception Conditions Directive and Dublin III Regulation embody the same key principles concerning the power of the judge called upon to assess the lawfulness of detention (§68). For this reason, it was possible to jointly examine the compatibility of Dutch legislation with regard to all these three instruments.

Subsequently, the AG presented briefly a set common rules concerning the judicial control of detention orders. He recalled in particular that detention of the TCN ordered by an administrative or judicial authority shall be subject to judicial review (§70). The requirement of judicial control serves primarily to protect the TCN against arbitrary deprivation of liberty (§72). Nonetheless, the rules concerning the extent of judicial control have not been harmonised so far at the EU level. The modalities of such a control are therefore covered by the principle national procedural autonomy of Member States (§73). The national legislation determining the extent of judicial control must nonetheless comply with the principles of effectiveness and equivalence. (§75).

Focusing on the assessment of  compatibility of national rule with the principle of effectiveness the AG briefly referred to the so called ‘procedural rule of reason test’ . According to this test, while examining the question of whether national procedural rule renders the application of EU law ‘impossible’ or ‘excessively difficult’, the judge must take account of ‘the role of that provision in the procedure, its conduct and its special features, viewed as a whole, before the various national bodies’ (see eg. XC and Others, C‑234/17, §49). In that context, must be considered, in particular, ‘the protection of the rights of the defence, the principle of legal certainty and the proper conduct of the procedure’ (XC and Others, C‑234/17, §49)

Yet, this test was not of particular relevance in the cases at hand, as the AG indicated that the ‘effectiveness requirement’ would not be satisfied if a procedural rule at stake was incompatible with the right to an effective judicial protection enshrined in Article 47 of the Charter (§78). The central problem in the Joined cases boiled down to the question of whether a national rule prohibiting ex officio assessment of conditions pertaining to detention infringed the right to an effective judicial protection.

The Court has ruled on different occasions that the principle of effectiveness ‘does not preclude a national provision which prevents national courts from raising of their own motion an issue as to whether the provisions of Community law have been infringed, where examination of that issue would oblige them to abandon the passive role assigned to them by going beyond the ambit of the dispute defined by the parties themselves’ (Van Schijndel, C-430/93 and C-431/93,§22). Yet, none of the so-far examined situations on ex-officio application of EU law has dealt directly with protection of the right to liberty guaranteed by Article 6 of the Charter (§80).

Relying on Mahdi case (C-146/14 PPU), the AG recalled that the Court assessing the lawfulness of the detention measures ‘must be able to take into account both the facts stated and the evidence adduced by the administrative authority and any observations that may be submitted by the third-country national’ (Mahdi, §62). He then drew attention to the paramount importance of the right to judicial protection in guaranteeing respect of the right to liberty (§86). Detention ordered on the basis of Return Directive, Reception Conditions Directive or Dublin III Regulation must respect the principle of proportionality and fundamental rights of the individuals concerned (§87).   

Plunging into the analysis of possible infringements on fundamental rights, the AG observed that the limitation on the scope of judicial control of detention measures constitutes a restriction of fundamental right to a remedy which shall be examined under Article 52 of the Charter. He underlined that the very essence of the right to effective judicial protection as well as protection against arbitrary detention would be infringed if the judge could not release a person detained even after having come to conclusion that detention was illegal (§91).

The impossibility for a judge to examine all relevant issues concerning the lawfulness of detention, may result in person being detained in situation where the conditions pertaining to detention are not (or are no longer) met (§92). This is inadmissible given that Article 15, paragraph 2, of the Return Directive and Article 9, paragraph 3, of the Reception Conditions Directive state clearly that when the detention is unlawful, the person concerned shall be released immediately. The release shall be thus an immediate consequence of finding that detention is illegal (§92).

The AG insisted again on the importance of the right to liberty and underlined that national procedural rules shall not allow doubts as to the lawfulness of detention to persist (§95). In a nutshell, the jurisdiction called upon to assess the lawfulness of detention order must control respect of general and abstract rules setting the conditions and modalities of detention. The limitation on the possibility for a judge to examine the issues and arguments which were not raised by the parties does not respect the principle of effectiveness. The Dutch legislation is incompatible with Article 15 of the Return Directive, Article 9 of the Reception Conditions Directive and Article 28 of the Dublin III Regulation read in conjunction with Articles 6 and 47 of the Charter.


Comments

The Opinion of AG de la Tour deserves attention for several reasons. Most importantly, the Joined cases would be the first occasion for the Court to directly adjudicate upon the question of an obligation to apply EU law ex officio in the context of detention of TCNs. Should the Grand Chamber follow the solution proposed by the AG, the judgement will be another example of the increasing influence of EU law on shaping national procedural rules in the field of migration (I). Furthermore, the Opinion sheds more light on the potential of EU fundamental rights to play a key role in setting limits of national procedural autonomy (II). 


Obligation of ex officio review of detention: a sign of ‘progressive revolution’ in the ECJ’s approach towards national procedural rules?  

The AG underscored the unprecedented nature of the subject-matter in the cases at hand.  This will be the first time when the Court will rule on the obligation of ex officio application of EU law in the context involving the application of the fundamental right to liberty (§1 and §80). As mentioned above, the Court has already stated that, in principle, national courts do not have obligation to raise points of EU law of their own motion. There are some exceptions to this rule, for instance in the field of consumer law (see eg. case Mostaza Claro, C-168/05). The AG proposed that in the situations concerning fundamental right to liberty the judge must proceed to assessment of all conditions pertaining to detention of his own motion, establishing thus a new exception to the rule on the lack of obligation to apply EU law ex officio. Importantly, the AG referred to obligation rather than a simple possibility for a national judge to review the lawfulness of detention on the grounds different from those relied on by the parties. In this regard, he opted for a more intrusive interference with the national procedural rules.

The creation of positive obligations and direct intervention into national procedures are a fairly rare phenomenon in the ECJ’s case law which has nonetheless become more visible in the recent years, at least as far as the field of migration and asylum law is concerned. Suffice it to mention for instance Országos (C‑924/19 PPU and C‑925/19 PPU) case in which Court stated that the national judge had to declare himself competent to examine detention measures decided by administrative body even though he did not have such a power under national law. In that judgement, the right to fundamental remedy enshrined in Article 47 of the Charter as well as in the relevant provisions of secondary law (Article 15 of Return Directive and Article 9 of Reception Conditions Directive 2013/33) played an eminent role in the Court’s reasoning.

Importantly, the developments regarding the significance of the right to an effective remedy in protection of procedural rights of migrants are not confined to the cases dealing with detention: they are also present in other areas of EU migration law. In a relatively recent case H. A. v État belge (C‑194/19)  concerning the scope of the right to a judicial remedy as guaranteed under Dublin III Regulation, the Court ruled that, when examining the lawfulness of transfer decision, the national judge shall be able to take due account of circumstances subsequent to the adoption of that decision. These findings were similarly the fruit of generous interpretation of the right to an effective remedy and a limited application of the doctrine of national procedural autonomy. Earlier, in the context involving the application of the Visa Code, building on the potential of Article 47 of the Charter, the Court interpreted the provision on the right to bring appeal against the refusal of visa (Article 32(3)) as requiring the establishment of judicial (and not solely administrative) remedy (El Hassani, C‑403/16). On several occasions, Article 47 of the Charter has thus served as a tool for unearthing the ‘creationist’ side of the principle of effective judicial protection which allows the Court to readjust or directly establish new remedies for the protection of rights guaranteed by EU law.

Given that, in the past, the Court directly conferred to national judges’ power to review the legality of detention (Országos), the imposition of duty to raise the point of EU law of their own motion would not constitute a revolutionary move in the Court’s case law on national procedural rules. Yet, cumulatively, case law on procedural rights and obligations is a significant step forward for enhanced protection of fundamental rights which may lead to renewal of the Court’s approach towards the doctrine of national procedural autonomy.


Concern for protection of fundamental rights as a key rationale for further limitation of national procedural autonomy in EU migration law

The principle of national procedural autonomy has traditionally been subject to requirements resulting from the principles of equivalence and effectiveness, subsequently complemented by the principle of effective judicial protection currently enshrined in Article 47 of the Charter. It has been argued that analysis focused on the respect of Article 47 of the Charter had a vocation to replace the ‘traditional test’ of effectiveness. The present opinion does not provide much clarification on the blurred relationship between effectiveness and effective judicial protection. The principle of national procedural autonomy, effectiveness and the ‘procedural rule of reason test’ are the starting point of the AG’s examination of compatibility of national legislation with EU law. Yet, very quickly the focus shifts towards the assessment of the effects the said legislation may have on the protection of fundamental right to liberty and right to a judicial remedy. All in all, fundamental rights-based analysis trumps the ‘procedural rule of reason test’. Whereas Article 47 constitutes a natural benchmark for assessing the compatibility of national procedural rules with EU law, the extensive reliance on the fundamental right to liberty in the AG’s reasoning illustrates a new trend in the field.

At the very beginning of his Opinion, AG de la Tour underlined that the importance of the right to liberty and the essential role of judges in protection of the latter justify a certain distrust (‘une certaine méfiance’) towards national procedural rules limiting the powers of judges (§1). The reasoning of the AG conspicuously marked by the concern for protection of the fundamental right to liberty (see in particular §86 and following).

On many occasions the AG refers to Article 6 of the Charter and to the provisions of secondary law concerning the detention conditions. The intrinsic links between the effective access to judge and adequate protection against arbitrary detention underlie a more demanding approach towards national procedural rules. The prominent role of the right to remedy in the protection of fundamental right to liberty justified the creation of obligation for national judge to examine the respect of all detention conditions of his own motion.

The Opinion illustrates that the concern for protection of fundamental rights may significantly affect the process of drawing the boundaries of national procedural autonomy. Presumably, in the future, the Court will leave less margin of manoeuvre for the application of national procedural rules in situations where the protection of EU fundamental rights is at stake. Such a stricter approach towards national rules could have been observed in previous case law. In the aforementioned cases Mahdi and Országos, the extension of powers of national judges served primarily as a mean of protection of fundamental right to an effective remedy and right to liberty. In those two cases however, the Court relied mostly on the sources of secondary law, making only minor references to Article 6 of the Charter. By contrast, the latter provision, together with Article 47 of the Charter constituted the very basis of the AG’s analysis. The Opinion confirms that the limitation of constantly shrinking area of national procedural autonomy may result not solely from the large scope Article 47 of the Charter but also, the necessity to protect substantive fundamental rights such as the right to liberty.

Finally, it is worth noting that, as the Council of State accurately pointed out (§39), ex officio examination of the conditions of lawfulness of detention has not been so far imposed by the European Court of Human Rights (‘ECtHR’). Assuming that the Court will follow the solution proposed by the AG, the standard of protection of fundamental right to liberty and right to an effective remedy under EU legal framework will be arguably higher than the one guaranteed within the system of the European Convention of Human Rights. In this regard, the joined cases at hand have potential to become another example of judgement in which the CJEU did not hesitate to go further than the ECtHR in terms of protection of basic freedoms of migrants.

It will be interesting to observe whether the Grand Chamber’s judgement in C, B and X will be, alike the AG’s Opinion, centred around the concern for protection of fundamental rights and whether such an approach would result in a more thorough review of national procedural rules. Should the ECJ decide to impose a new duty to national judges, the judgement will confirm the tendency in recent case law on adjusting the application of national procedural rules for the sake of protecting the fundamental rights. Independently of the of the outcome of the judgement, the Opinion of AG de la Tour confirms that Article 47 of the Charter has already become as a powerful tool for boosting effective judicial protection, in particular in situations where it is relied upon for purposes of securing the respect of substantive fundamental rights.